Key Takeaways
- What it takes: A production smart contract moves through eight stages, from writing the business rules down to post-deployment monitoring. The code itself is rarely the slow part. Specification and audit are.
- Where projects fail: Platform choice and security review. Picking a chain that does not match your throughput or compliance needs locks in the wrong costs, and skipping an audit is how Ronin lost $625 million.
- What is different in 2026: Layer 2 rollups cut transaction fees by more than 90 percent against early Ethereum, audit tooling caught up, and Solidity, Rust and Move each own a clear slice of the market.
Smart contract development is the process of turning a business agreement into code that runs on a blockchain and executes itself when its conditions are met. The work spans eight stages: defining the rules, choosing a chain, writing the contract, testing it, auditing it, deploying to mainnet, and monitoring it afterwards.
That definition is easy. Shipping one that holds real money is not.
Most teams arrive at this with a working idea and no sense of the order things happen in. They write Solidity before they have written the conditions down in plain English. They pick Ethereum because it is the name they know, then discover their app needs throughput Ethereum mainnet was never built to give them. They budget for development and forget the audit, which on a contract holding user funds is not optional.
This guide walks the whole path in order. You get what smart contracts are and how they actually execute, the five types you will run into, a step by step build process, a platform comparison across the seven chains worth considering in 2026, what security review costs and why, realistic timelines, and where this is all heading. The global smart contracts market reached $3.21 billion in 2025, up from $2.63 billion the year before, a 22 percent compound growth rate. The tooling has matured with it.
What Are Smart Contracts?
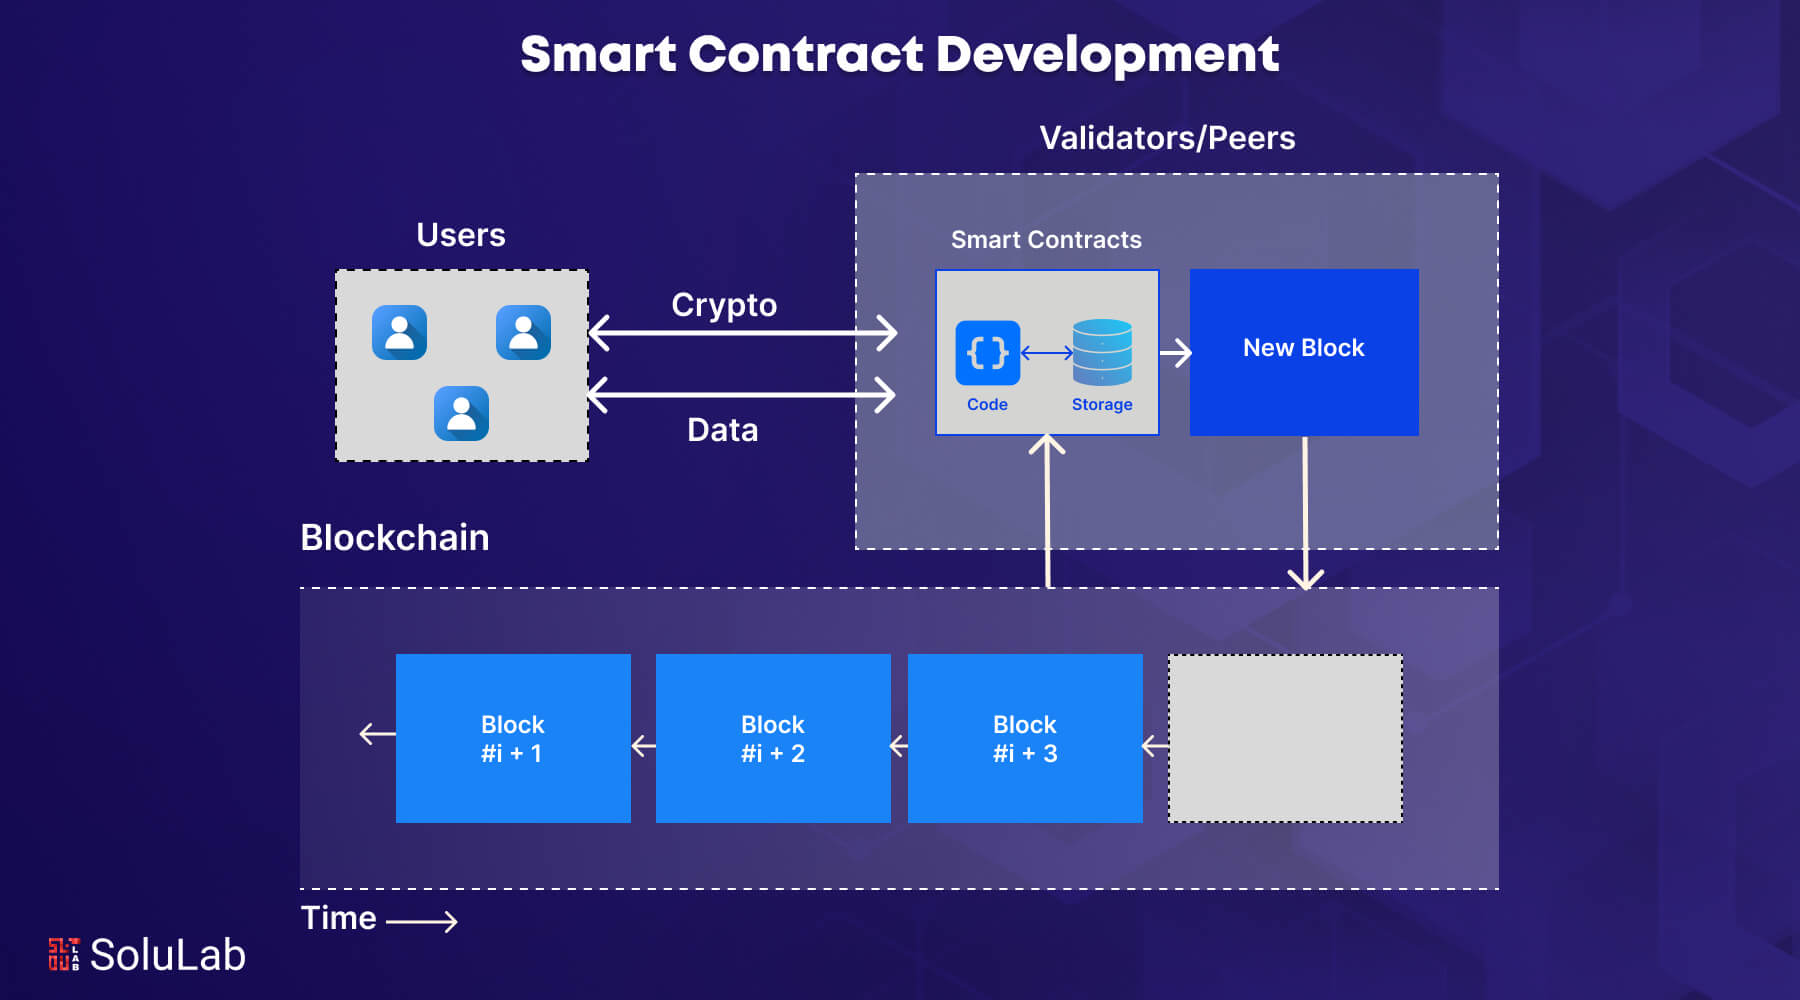
A smart contract is a program stored on a blockchain that runs when predetermined conditions are met. It holds the terms of an agreement in code rather than in prose, and it enforces those terms itself, without a bank, a notary or an escrow agent standing in the middle.
The mechanics are simpler than the reputation suggests. You write a set of if-then rules. You deploy them to a network such as Ethereum, where the code gets a permanent address. From that point the contract sits there and waits. When someone sends it a transaction that satisfies a condition, the network runs the matching instruction and records the result on the ledger. Every node agrees on what happened, because every node ran the same code against the same state.
A concrete example helps. Say a buyer and a seller agree that payment releases when a shipment is scanned at its destination. In the traditional version, a person checks the scan, a second person approves the release, and a bank moves the funds a day or two later. In the smart contract version, an oracle feeds the scan event on-chain, the contract sees its condition satisfied, and the funds move in the same block. Nobody approves anything, because there is nothing left to approve.
Two properties make this work, and both come from blockchain technology rather than from the contract itself. The code cannot be quietly edited after deployment, and its execution history is visible to every participant. That is why parties who do not trust each other can still rely on the outcome. They are not trusting a counterparty. They are trusting code they both read before it went live.
How Do Smart Contracts Work?
A smart contract moves through six stages from agreement to permanent record. The sequence matters, because most costly mistakes happen in the first two stages and only become visible in the last one. It helps to understand how blockchain works underneath, since the guarantees at each stage come from the ledger rather than from the contract.
- Agreement. The parties settle what the contract does and, more importantly, what counts as a trigger. A date passing. A payment clearing. A signature arriving from a specific address. Anything the chain can verify on its own.
- Coding. Those terms get written in a contract language, usually Solidity on Ethereum-compatible chains or Rust on Solana. This is where ambiguity in stage one turns into a bug.
- Deployment. The compiled bytecode is published to the network in a transaction, exactly like a cryptocurrency transaction. Once it confirms, the contract has an address and the code at that address is fixed.
- Condition monitoring. The contract watches for the inputs it was told to watch for. On-chain events it can see directly. Off-chain facts, such as a price or a delivery confirmation, have to be delivered by an oracle.
- Execution. A trigger arrives and the matching branch runs. Funds transfer, ownership records update, a token mints. The network charges gas for the computation and the state changes atomically, meaning it either completes fully or reverts entirely.
- Recording. The result is written into a block. It stays there, readable by anyone, for as long as the chain exists. There is no amended version and no retraction.
Step five carries a detail worth sitting with: immutability cuts both ways. A contract that behaves correctly will keep behaving correctly forever. A contract with a logic flaw will keep executing that flaw forever, on every call, and you cannot patch it in place. That single property is the reason the build process below front-loads so much specification and review work.
Read More: What Problems Do HTLC Smart Contracts Solve in Crypto Payments?
Types of Smart Contracts
Not every smart contract does the same job, and the type you are building changes the language, the audit scope and the regulatory questions you will face. Five categories cover almost everything in production today.
- Smart legal contracts. A conventional legal agreement with self-executing logic attached. The prose still governs the relationship, but the payment, renewal or penalty clauses run in code. These carry the heaviest compliance load, because the contract has to satisfy a court as well as a compiler.
- DAO contracts. The governing code for a Decentralized Autonomous Organization. Membership, proposals, voting weights and treasury rules all live on-chain, which is how a group of people coordinates money without a board or a bank account.
- Application logic contracts. The working parts behind a decentralized app. Matching engines, lending pools, game state, access control. Most of the code a development team writes falls in this bucket, and so does most of the attack surface.
- Token contracts. Rules for creating, moving and destroying a digital asset, whether that is a fungible token or a Non-Fungible Token. Standards such as ERC-20 and ERC-721 mean you rarely start from zero here, and you should not.
- Marketplace contracts. Escrow, settlement, fee splits and reputation for decentralized trading. They hold funds belonging to strangers during a trade, which puts them among the highest-risk contracts you can deploy.
Key Components of a Smart Contract
Strip away the vocabulary and three things have to work together for any contract to function.
- Conditions and logic. The if-then rules that define what triggers the contract and what it does in response. Get the logic wrong and you get an outcome nobody intended, permanently. Precision here matters more than anything else in the build.
- Digital signatures. Each party proves identity with a cryptographic signature. Not a scanned signature or a click, but mathematical proof tied to a private key, which cannot be forged and leaves a permanent record on the ledger.
- Blockchain integration. The contract and every action it takes are recorded on a decentralized ledger. That record cannot be deleted, edited or hidden, which is the entire point of putting the agreement there in the first place.
Smart Contracts vs Traditional Contracts
The difference is easier to see side by side, across the dimensions that actually affect a business.
| Dimension | Traditional Contract | Smart Contract |
|---|---|---|
| Execution | Manual, someone has to act | Automated, runs the moment conditions are met |
| Intermediaries | Lawyers, banks, notaries | None, the code enforces itself |
| Speed | Days to weeks | Seconds to minutes |
| Cost | Legal fees plus admin overhead | Gas fees only, fractions of a cent on Layer 2 |
| Transparency | Private between parties | On-chain, visible to all network participants |
| Error risk | High, humans interpret terms differently | Low at runtime, but a coding error is permanent |
| Auditability | Paper trail, often incomplete | Full immutable on-chain record |
| Enforceability | Jurisdiction-dependent | Code-enforced, consistent across borders |
| Amendability | Parties sign an addendum | Requires a planned upgrade pattern, decided before launch |
Read the last two rows together. A smart contract gives you enforcement that does not care which country the counterparty sits in, and takes away your ability to renegotiate after the fact. For a cross-border settlement that is a clear win. For an agreement you expect to revise every quarter, it is a reason to think carefully about upgrade patterns before you deploy, not after.
Read Blog: Benefits of Blockchain-as-a-Service?
How to Develop a Smart Contract: The 8 Steps
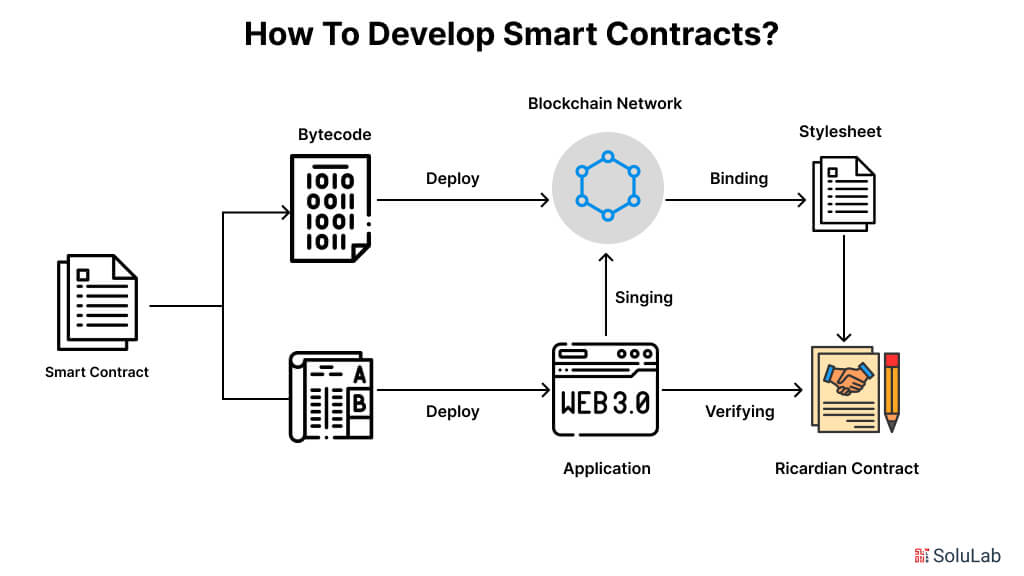
What follows is the order a production build actually runs in. Teams that skip ahead to step five almost always come back to step one later, at much greater cost.
1. Define the business requirement
Start by naming what the contract replaces. Which manual step goes away, who currently performs it, and what does it cost in time or error rate. If you cannot answer that, the contract is a technology exercise rather than a business one. This is also where you decide what stays off-chain, which is usually more than teams expect.
2. Specify the contract terms
Write the rules in plain language before anyone opens an editor. Who are the parties, what are the exact conditions, what happens when a condition is met, and what happens when one is never met at all. That last question catches more bugs than any testing framework. A contract with no path for the unhappy case will sit holding funds forever.
3. Select the blockchain network
Now match the requirement to a chain, weighing throughput, fees, finality, developer availability and compliance posture. The comparison further down covers the realistic options. For permissioned enterprise work where data cannot be public, Hyperledger Fabric is the usual answer rather than any public chain. It is worth reviewing the wider blockchain platform field before committing, because this decision sets your cost structure for years.
4. Choose a programming language
The chain narrows this considerably. Solidity covers Ethereum and every EVM-compatible network, which is most of the market. Rust is the path on Solana, Polkadot and NEAR. Move is used on Aptos and Sui. Vyper is a deliberately restricted Python-like alternative on the EVM, chosen by teams who want a smaller surface for mistakes.
5. Write the contract code
Build on audited libraries rather than from scratch. OpenZeppelin implementations of token standards, access control and upgrade proxies have been reviewed by more people than any new codebase ever will be. Keep functions short, keep state changes before external calls, and decide early whether the contract is upgradeable. Retrofitting an upgrade pattern after deployment is not possible.
6. Test the smart contract
Unit tests for each function, integration tests against a fork of mainnet state, and fuzz testing to push values a human tester would not think to try. Foundry and Hardhat both do this well. Aim to exercise every revert path, not just the happy one, and run a gas profile while you are there so costs do not surprise you in production.
7. Deploy the contract
Testnet first, always, with the same deployment script you will use on mainnet. Verify the source code on the block explorer so anyone can read what they are interacting with. Confirm constructor parameters twice, because a wrong owner address or fee recipient set at deployment is permanent on a non-upgradeable contract.
8. Monitor and maintain
Deployment is not the finish line. Set up on-chain monitoring for unusual transaction patterns, keep an incident runbook with a named person who can pause the contract if it has a pause function, and track the libraries you depend on for disclosed vulnerabilities. Contracts holding value need an owner in the operational sense, not just the cryptographic one.
The smart contract development lifecycle
Specification and audit consume most of the calendar time. Writing the contract rarely does.
Smart Contract Programming Languages
Language choice follows chain choice, and it drives what your hiring looks like. Solidity developers are plentiful. Rust and Move specialists cost more and take longer to find.
| Language | Runs on | Why teams pick it | Trade-off |
|---|---|---|---|
| Solidity | Ethereum and all EVM chains | Largest talent pool, deepest tooling, most audited libraries | Flexible enough to let you write unsafe patterns |
| Rust | Solana, Polkadot, NEAR | Memory safety and high performance on fast chains | Steep learning curve, smaller hiring pool |
| Vyper | EVM chains | Restricted by design, easier to reason about and review | Fewer features and a much smaller ecosystem |
| Move | Aptos, Sui | Resource model makes asset duplication hard at the language level | Newest of the group, limited third-party libraries |
| Go and JavaScript | Hyperledger Fabric | Familiar to enterprise teams, no new language to learn | Permissioned networks only, not public chains |
Best Smart Contract Platforms in 2026
Platform choice shapes everything downstream: developer costs, transaction fees, compliance options and how far you can scale. There is no universal right answer, only a fit against your throughput needs, your regulatory constraints and the skills your team already has.
Four criteria separate the options in practice. Can it carry your transaction load without degrading. Does it give you real defenses and a track record to check them against. Can your developers get productive quickly, or does every build fight them. And how healthy is the surrounding ecosystem of tools, documentation and people who answer questions at 2am. That last one rescues more projects than teams admit.
| Platform | Language | Best for | 2026 notes |
|---|---|---|---|
| Ethereum and Layer 2 | Solidity | DeFi, NFTs, enterprise pilots | Rollups such as Arbitrum and Base cut fees by more than 90 percent, largest developer pool by a wide margin |
| Solana | Rust | High-throughput consumer apps | Fast and cheap, but requires Rust specialists who cost more to hire |
| BNB Smart Chain | Solidity (EVM) | Cost-sensitive DeFi projects | EVM-compatible, straightforward migration path from Ethereum |
| Cardano | Plutus (Haskell) | Research-led and regulated deployments | Strong formal security model, smaller ecosystem and talent pool |
| Polkadot | Rust and ink! | Cross-chain and interoperability work | Parachains allow specialised, application-specific deployments |
| Avalanche | Solidity (EVM) | Enterprise subnets | Permissioned subnet model suits regulated use cases |
| Tezos | Michelson and SmartPy | Long-lived contracts needing upgrades | On-chain governance ships upgrades without hard forks |
| Hyperledger Fabric | Go, JavaScript | Private enterprise chains | The default where data cannot be public and membership must be controlled |
Ethereum
Ethereum remains the default, and in 2026 it is still the most used platform of the group. The tooling is mature, the developer community runs deep, and its security properties are well understood because they have been tested under real attack for a decade. You get EVM compatibility, broad dApp support, a working Layer 2 ecosystem for scaling, and decentralized governance.
Mainnet fees are still the highest of any chain here, which is precisely why the rollup layer exists. Most new consumer applications deploy to Arbitrum, Base or Optimism and settle to Ethereum underneath. If you want a foundation that has already survived what the others have yet to face, this is it.
BNB Smart Chain
BNB Smart Chain is fast, cheap to transact on, and EVM-compatible, so Solidity code and Ethereum tooling port across with little friction. Its infrastructure relies on stable node access, which is why teams typically run against a managed endpoint such as a BSC RPC provider rather than self-hosting from day one.
It suits affordable DeFi, NFT platforms and products that need to ship quickly on a startup budget. The trade-off is a smaller validator set than Ethereum, which buys speed at some cost to decentralization. Whether that matters depends entirely on what your contract holds.
Cardano
Cardano takes the research-first route, building on peer-reviewed academic work before shipping. Underneath sits Ouroboros, a proof-of-stake consensus protocol, and the platform supports formal verification of contract behaviour.
That makes it a fit for the long game: education, healthcare, government work, anywhere stability and provable correctness matter more than shipping this quarter. The cost is a smaller developer ecosystem and a functional programming model that takes time to learn.
Solana
Speed is Solana‘s identity. Transactions confirm in well under a second and fees are a fraction of a cent, which is why consumer applications and NFT projects keep landing there when other chains slow under load. Its Proof of History mechanism is what allows that throughput.
Two things to weigh. Contracts are written in Rust, so your hiring is harder and slower than an EVM build. And the account model is genuinely different from Ethereum’s, which means porting an existing Solidity contract is a rewrite rather than a migration. Teams that deploy smart contracts on blockchain networks like this one plan for that gap up front.
Polkadot
Polkadot was built for a different problem: getting separate blockchains to work together. Its parachain architecture gives each application its own chain while sharing security from the relay chain underneath.
It fits cross-chain applications and enterprises that want a purpose-built chain without running their own validator set. The complexity is real, though. You are designing a chain, not just a contract, and that is a larger commitment than most projects need.
Avalanche
Avalanche pairs high performance with near-instant finality and low energy draw. The pieces that matter are subnets for scaling, Ethereum compatibility through the C-Chain, and the option to run a permissioned subnet with your own validator rules.
That subnet model is the reason regulated businesses look at it. You get EVM tooling and a controlled membership set at the same time, which is a combination Ethereum mainnet cannot offer and Hyperledger Fabric offers only by giving up the public ecosystem entirely.
Tezos
Tezos upgrades itself. Its on-chain governance ships protocol changes without a hard fork, so the network adapts over years instead of splitting the community each time something significant changes. Formal verification is supported for high-stakes contracts.
Fees stay low and the proof-of-stake consensus is light on power. It lands best with teams who expect their contracts to live a long time and want a documented path for changing them.
If the platform decision still feels open after all that, it usually means the requirement is not yet specific enough about throughput and compliance. A blockchain consulting session with someone who has shipped on several chains tends to resolve it in an hour, and it is a far cheaper hour than a migration. The same reasoning applies when you build decentralized applications on top of whichever chain you land on.
Smart Contract Security and Auditing
This is the section most first-time projects underbudget, and it is the one that decides whether the others mattered.
Because deployed code cannot be edited, a flaw is not a bug you fix next sprint. It is a permanent property of the contract, open to anyone who reads the bytecode. Attackers do read it. The Ronin Network bridge lost $625 million. Poly Network lost $611 million. Behind those two sit a long tail of smaller protocols that quietly stopped operating after a single exploited function.
An independent review from a smart contract audit company typically runs $5,000 to $40,000 depending on contract complexity and how much value it will hold. Set against the numbers above, that is cheap. The smart contract audit cost is still the most commonly cut line item in a first deployment, and cutting it is the single clearest predictor of a bad outcome.
What a real audit covers, beyond a tool run:
- Reentrancy and external call ordering. The classic failure, where a contract calls out before updating its own state and the callee calls straight back in.
- Access control. Which addresses can call privileged functions, and what happens if the owner key is lost or stolen.
- Oracle and price manipulation. Whether a single-block price move or a flash loan can push the contract into a state it was never meant to reach.
- Arithmetic and edge values. Zero amounts, maximum values, rounding that quietly favours one party over thousands of transactions.
- Upgrade and pause mechanisms. If they exist, they are also an attack surface. If they do not, the incident response plan has to work without them.
Run your own pass against a smart contract audit checklist before you commission the external review. Fixing the obvious findings in advance keeps the auditor focused on the subtle ones, which is what you are actually paying for. If the contract will hold user funds and you do not have this capability in-house, this is the point to bring in a smart contract development company that carries both the build and the security review, rather than assembling the two separately after the code is written.
How Long Does Smart Contract Development Take?
A single, straightforward contract built on an established standard takes roughly one to three weeks to write and test. That figure is where most published estimates stop, and it is why so many first budgets are wrong. It covers the coding only.
| Scope | Realistic timeline | What drives it |
|---|---|---|
| Single standard contract, for example an ERC-20 token | 1 to 3 weeks | Built on audited libraries, limited custom logic |
| Custom contract with business-specific rules | 4 to 8 weeks | Specification work and test coverage, not the coding |
| Multi-contract system, for example a DeFi protocol or marketplace | 3 to 6 months | Contract interactions, oracle design, economic modelling |
| External security audit | 2 to 6 weeks on top | Auditor availability, findings, fix cycle, re-review |
Four factors move these numbers more than anything else: how precisely the requirements were written before coding started, whether the team has shipped on the chosen chain before, how much of the logic can sit on audited libraries rather than custom code, and how long the audit queue is when you are ready to book it. That last one is scheduling rather than engineering, and it is routinely forgotten until it adds a month.
Smart Contract Use Cases by Industry
The pattern repeats across sectors. Wherever there is a multi-party agreement, a conditional payment or a traceability requirement, a smart contract usually beats the manual process it replaces. The blockchain development use cases below are running in production today, not in pilot.
- Financial services. Loan disbursement, automated insurance payouts and cross-border settlement, all triggered by predefined conditions with no clerk watching a clock. Lending protocols handle collateral and liquidation entirely in code.
- Real estate. Purchases execute once payment clears and legal conditions are confirmed. The work brokers and notaries do separately collapses into one process, and a closing that took a week takes hours.
- Supply chain. Every handoff is authenticated and logged on-chain. Payment releases to each party on delivery, and stock falling below a threshold can trigger a reorder automatically. Retailers can prove provenance, suppliers cannot dispute the ledger.
- Healthcare. Patient consent encoded in a contract governs exactly who can read which records under which conditions, with compliance built into the architecture rather than bolted on afterwards.
- Insurance. Parametric policies pay out on a verifiable trigger, a flight delay or a weather reading, without a claims process at all. The assessment cost disappears because there is nothing to assess.
- Legal. Routine execution, escrow release and dispute triggers run automatically, leaving lawyers on the work that needs judgement rather than the work that needs a signature.
Read Also: Why AI Smart Contracts Are the Future of Business?
What Is Changing in Smart Contract Development in 2026
The concept has not changed since Ethereum launched in 2015. The maturity around it has, and four shifts matter for anyone planning a build this year.
- Layer 2 economics changed what is buildable. Rollups brought transaction costs down by more than 90 percent against early Ethereum. Applications that made no sense at $20 a transaction, micropayments, on-chain gaming, high-frequency settlement, are now routine. If your last cost model was built before rollups matured, rebuild it.
- Cross-chain execution became practical. Chainlink’s CCIP, Polkadot’s relay chain and the Cosmos IBC protocol let a contract on one chain trigger action on another. That removes the fragmentation that held enterprise adoption back, and it means chain choice is no longer quite as permanent as it was.
- Oracles widened what contracts can respond to. A contract that only sees on-chain data is limited by definition. Networks such as Chainlink and Pyth feed prices, weather, shipment confirmations and identity attestations directly into contract logic, which is what makes parametric insurance and real-world asset products work at all.
- Governance replaced the upgrade dilemma. Changing a deployed contract used to mean choosing between breaking the system and freezing it forever. DAO governance models let token holders vote upgrades through a transparent on-chain process, so contracts evolve without asking users to trust a single key holder.
Taken together these push in one direction. The hard part of smart contract work is moving away from making the code run and towards deciding what it should do, who can change it, and what it is allowed to see. That is a specification problem, which is where this guide started.

Conclusion
Smart contract development rewards the work you do before you write any code. Specification, platform fit and security review decide the outcome. The coding, which is what most teams start with, is rarely where projects fail.
If you take three things from this guide, take these. Write the rules in plain language until there is no ambiguity left, including what happens when the condition is never met. Choose the chain against your actual throughput and compliance requirements rather than its reputation. And budget the audit as part of the build, not as an optional extra, because immutability means a flaw you ship is a flaw you keep.
SoluLab builds and audits smart contracts across Ethereum, Solana, Polygon, Avalanche and Hyperledger, from a single agreement through to enterprise governance systems. If you want a second opinion on architecture before committing, or a team to take the build end to end, talk to our blockchain engineers. You can also Hire Blockchain Experts for a specific chain or a defined piece of work instead of a full engagement.
Smart contract development is the process of turning a business agreement into code that runs on a blockchain and enforces itself. It covers defining the rules, choosing a chain and language, writing and testing the contract, commissioning a security audit, deploying to mainnet, and monitoring the contract once it is live.
The contract waits at a fixed address for an input that satisfies one of its conditions. When that input arrives, the network runs the matching branch of code, charges gas for the computation, and writes the resulting state change into a block. Execution is atomic, so it either completes in full or reverts entirely.
Three parts have to work together. Conditions and logic define the if-then rules that trigger the contract. Digital signatures prove which party authorised each action using cryptographic keys. Blockchain integration records the contract and every action it takes on a ledger that cannot be edited or deleted afterwards.
Define the business requirement, specify the terms in plain language, select the blockchain network, choose a programming language, write the contract against audited libraries, test it including every failure path, deploy to testnet then mainnet, and set up monitoring. Specification and audit take most of the calendar time, not the coding.
Solidity is the most widely used, covering Ethereum and every EVM-compatible chain. Rust is used on Solana, Polkadot and NEAR. Move runs on Aptos and Sui. Vyper is a deliberately restricted alternative on the EVM. Hyperledger Fabric uses Go or JavaScript for permissioned enterprise networks.
Ethereum with its Layer 2 rollups leads on tooling and developer availability. Solana suits high-throughput consumer apps, BNB Smart Chain suits cost-sensitive DeFi, Cardano and Tezos support formal verification, Polkadot handles cross-chain work, Avalanche offers enterprise subnets, and Hyperledger Fabric covers private permissioned deployments.
Weigh four things against your requirement: transaction throughput, security track record, how quickly your developers can become productive, and the health of the surrounding tooling and community. Compliance constraints usually decide it fastest. If data cannot be public, a permissioned network such as Hyperledger Fabric is the realistic option.
A single standard contract such as an ERC-20 token takes one to three weeks. A custom contract with business-specific rules runs four to eight weeks. A multi-contract system such as a DeFi protocol takes three to six months. An external security audit adds a further two to six weeks on top.
Cost tracks scope and chain. A single standard contract is the cheapest case, while a multi-contract protocol with custom economics costs substantially more. Budget the security audit separately, at roughly $5,000 to $40,000 depending on complexity and how much value the contract will hold in production.
An independent reviewer reads the contract line by line and runs automated analysis, checking reentrancy, access control, oracle manipulation, arithmetic edge cases and upgrade mechanisms. Findings are returned by severity, your team fixes them, and the auditor re-reviews the changes. Run your own checklist pass first so the audit focuses on subtle issues.
Not directly. Deployed code is immutable, which is what makes it trustworthy. Teams that need to make changes build an upgrade pattern in before launch, usually a proxy contract that points to replaceable logic. That decision has to be made ahead of deployment, because it cannot be retrofitted afterwards.
A traditional contract is prose that people interpret and enforce through courts and intermediaries, taking days or weeks. A smart contract is code that enforces itself the moment its conditions are met, in seconds, with no intermediary. The trade-off is that you cannot renegotiate it after deployment the way you can amend a signed document.
Bhavya is driving growth through data-backed demand generation for AI and Web3 solutions. With 9+ years in digital marketing, he has spearheaded initiatives that led to a 40% increase in qualified inbound leads. Bhavya shares insights on marketing ROI and scaling a digital presence via AI workflows. He is open to connecting with startups and enterprise teams to help them overcome their challenges.